By using this site, you agree to the Privacy Policy and Terms of Use.
Accept
Media HydeMedia Hyde
  • Home
  • Politics
  • Education
  • Entertainment
  • Sports
  • Blogs
  • Business & Commerce
  • Others
    • Religious
    • Metropolitan
    • Climate and Weather
Font ResizerAa
Media HydeMedia Hyde
Font ResizerAa
  • Home
  • Politics
  • Education
  • Entertainment
  • Sports
  • Blogs
  • Business & Commerce
  • Others
    • Religious
    • Metropolitan
    • Climate and Weather
Follow US
© 2026 Media Hyde Network. All Rights Reserved.
Cyber SecurityHeadline

Microsoft uncovers massive phishing campaign exploiting ASCII smuggling technique

Last updated: September 8, 2026 1:10 am
Haris Ali
Share
Microsoft uncovers massive phishing campaign exploiting ASCII smuggling technique
SHARE

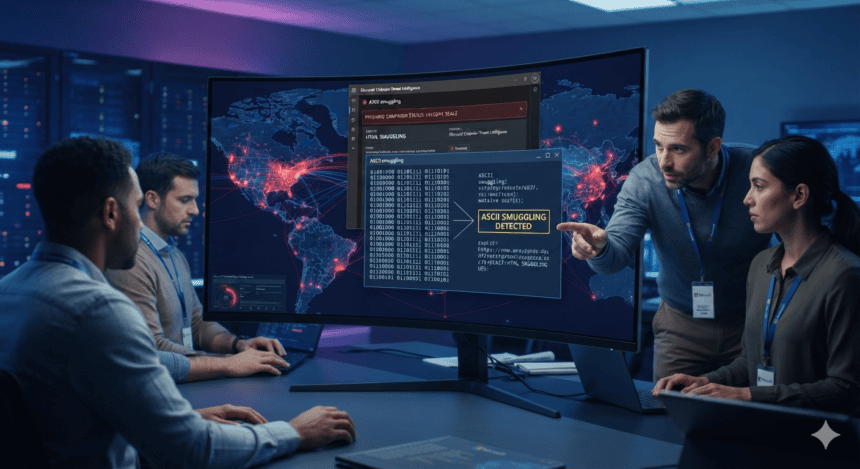
Microsoft’s security team has identified a sophisticated phishing operation that bypasses traditional email security filters by using a technique known as “ASCII smuggling.” The campaign, which targets corporate credentials, leverages HTML and CSS to hide malicious code in plain sight, rendering standard signature-based detection tools ineffective.

The attack works by smuggling a malicious payload inside a seemingly benign HTML file. By using specific character sets and encoding tricks, the attackers force the victim’s browser to reconstruct the malicious script locally. Because the code is fragmented and disguised during the transit phase, secure email gateways—which scan for known signatures—see nothing but harmless text.

“The technique relies on the browser’s ability to interpret specific HTML attributes in ways that security filters don’t,” said a senior threat researcher involved in the investigation. “It’s not a vulnerability in the browser itself, but a clever abuse of how web pages are rendered.”

Once the victim opens the attachment, the browser assembles the hidden script. This script then triggers a fake login page designed to look exactly like the target company’s Microsoft 365 or Google Workspace portal. The goal is simple: harvest credentials in real-time.

This campaign isn’t targeting random individuals; it’s focused on high-value corporate targets. Microsoft noted that the attackers are using legitimate-looking lures—invoices, shipping notifications, and internal HR memos—to lower the guard of employees. Once a user enters their password, the data is funneled directly to an attacker-controlled server.

The surge in these attacks has forced IT departments to rethink their perimeter defenses. Traditional “block lists” for malicious URLs are failing because the phishing pages are often hosted on compromised, reputable domains that haven’t been flagged yet.

Security experts are now pushing for a shift toward “zero-trust” authentication. If a company relies solely on a password, they’re already losing. Organizations are being urged to mandate hardware-based security keys or FIDO2-compliant authentication methods, which render stolen passwords useless to attackers.

Microsoft’s findings underscore a growing trend in cybercrime: attackers are moving away from brute-force exploits and toward creative manipulation of standard web protocols. As long as browsers prioritize rendering complex HTML, attackers will find new ways to hide their tracks within the code.
Share This Article
Email Copy Link Print
Previous Article Petrol Prices Spike as Government Scrambles to Meet IMF Targets Petrol Prices Spike as Government Scrambles to Meet IMF Targets
Next Article 480 Newborn Deaths in Eight Months: Mithi Hospital Crisis Deepens 480 Newborn Deaths in Eight Months: Mithi Hospital Crisis Deepens
Leave a Comment

Leave a Reply Cancel reply

Your email address will not be published. Required fields are marked *

Sponsored Ads

Stay Connected

FacebookLike
XFollow
InstagramFollow
YoutubeSubscribe
WhatsAppFollow
ThreadsFollow
Lahore Police Tighten Security Around Girls’ Colleges and Universities
Education
October 24, 2026
Sindh Government Launches Inquiry Into Hyderabad Board Exam Results
Education
October 24, 2026
Historic Multan Library Reopens After Restoration
Education
October 24, 2026
Punjab Opens MBBS Admissions at Private Medical Colleges for 2026–27
Education
October 24, 2026
Hemophilia Society Plans District-Level Awareness and Screening Drive in Hyderabad
Health
October 24, 2026
Flu Vaccine Shortage Raises Concerns as Mustafa Kamal Addresses Supply Issues
Health
October 24, 2026

You Might Also Like

Explosion at Qatar Gas Plant Leaves 54 Injured
Court & CrimeHeadline

Explosion at Qatar Gas Plant Leaves 54 Injured

By
Ayesha Masood
Pakistan Seeks Singapore’s Support in Repatriating Nationals, Iranians Aboard Vessels Seized by US
HeadlinePolitics

Pakistan Seeks Singapore’s Support in Repatriating Nationals, Iranians Aboard Vessels Seized by US

By
Ayesha Masood
Sindh on high alert as new monsoon spell approaches
Climate and WeatherHeadline

Sindh on high alert as new monsoon spell approaches

By
Ayesha Masood
Trump hosts crypto contest winners at Mar-a-Lago as his coin languishes
Business & CommerceHeadline

Trump hosts crypto contest winners at Mar-a-Lago as his coin languishes

By
Ayesha Masood
Media Hyde Media Hyde Dark
Facebook Twitter Youtube Rss Medium

About US

Media Hyde Network: Your instant connection to breaking stories and live updates. Stay informed with our real-time coverage across politics, tech, entertainment, and more. Your reliable source for 24/7 News.

Top Categories
  • Headline
  • Politics
  • Entertainment
  • Education
  • Sports
  • Religious
  • Metropolitan
  • Climate and Weather
Usefull Links
  • Contact Us
  • Disclaimer
  • Privacy Policy
  • Cookies Policy
  • Advertising Policy
  • Terms & Conditions

© 2025 Media Hyde Network. All Rights Reserved.

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?